How ScamShield AI Flagged a Business Email Compromise Attempt on an Indian Exporter
A Surat exporter nearly lost Rs 15.4 lakh to a Business Email Compromise attack. ScamShield AI caught the spoofed email before the payment was made.
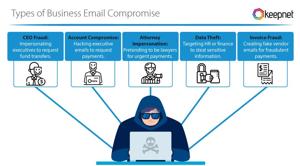
Note: This is a representative case study based on real Business Email Compromise (BEC) fraud patterns targeting Indian exporters and SMEs. Details are anonymised.
Background
In January 2026, a garment exporter based in Surat received an email that appeared to come from their UK buyer. The email requested a change in bank account details for the upcoming invoice payment of USD 18,500 (approximately Rs 15.4 lakh).
The email looked identical to previous genuine communications. The buyer's name was correct. The email signature matched. Even the email thread history appeared legitimate.
The Problem
The accounts team at the exporting firm forwarded the email to their CA for processing. Before acting on the bank detail change, the CA firm ran the sender email address through ScamShield AI as part of their new vendor and payment verification protocol.
What ScamShield AI Detected
The risk scan returned a CRITICAL RISK rating within seconds. The findings were:
The sender domain (buyer-company.co.uk) had been spoofed. The actual sending domain was buyer-company.co.uk.mail-dispatch.net, a lookalike domain registered just 6 days prior.
The email headers showed the message originated from a server in Eastern Europe, not the UK.
The new bank account details pointed to a recently opened account in a different country than the buyer's registered address.
The email body used language patterns consistent with known BEC fraud templates in ScamShield AI's database.
The Outcome
The CA firm immediately contacted the UK buyer through a phone number on record (not the one in the email). The buyer confirmed they had sent no such instruction and were completely unaware their identity had been impersonated.
The payment was held. The exporter preserved Rs 15.4 lakh and filed a cybercrime report. The UK buyer also initiated their own investigation.
Why BEC Attacks Are Especially Dangerous for Indian Exporters
Business Email Compromise is the highest-value cyber fraud targeting Indian SMEs in 2026. It does not rely on malware or technical exploits. It exploits trust. Attackers monitor email threads for weeks before striking, timing the attack to coincide with a large legitimate payment.
Traditional antivirus and spam filters cannot detect BEC attacks because the emails contain no malicious links or attachments.
How ScamShield AI Stops BEC
ScamShield AI analyses the sender email domain, header metadata, language patterns, and cross-references against known BEC fraud templates. It catches what the human eye and spam filters miss.
If your business makes international or high-value domestic payments, integrate ScamShield AI into your payment approval process. Start your free screening at scamshieldai.in.